

Article · part of a guide
Getting Started with Terraform Vulnerability Scanning
Terraform vulnerability scanning is the practice of automatically analyzing infrastructure code to find & fix security issues before they reach production.
Key takeaways
- Terraform vulnerability scanning automatically analyzes infrastructure code to find and fix security issues before they reach a production environment.
- The most common Terraform security risks are misconfigurations: open security groups exposing ports like SSH, hardcoded secrets, and unencrypted data storage.
- tfsec, Checkov, Terrascan, and Trivy are mature open-source scanners, each with a different focus from Terraform-native speed to multi-framework compliance.
- Scanners are most effective when run inside a CI/CD pipeline as a security gate that blocks merges, not just on a developer laptop.
- Scanning is the prevention layer and pairs with policy-as-code and drift detection for a complete security loop.
This post is part of a series on IaC Security: Securing Your Terraform and OpenTofu Infrastructure.
Terraform vulnerability scanning means automatically analyzing your infrastructure code to find and fix security issues before they ever reach a production environment. If your team cares about cloud security, it's one of the first things to set up, and it works the same way for Terraform and OpenTofu.
What Misconfigurations Does Terraform Vulnerability Scanning Catch?
The most common risks in Terraform are misconfigurations you could have prevented, and small mistakes like these cause big breaches. These are some of the issues scanners catch most often.
Catch Insecure Network Access
One of the most common mistakes is creating a firewall rule or security group that exposes a sensitive port, like SSH (22), to the entire internet.
Insecure HCL Example:
# This security group allows SSH access from ANY IP address.
resource "aws_security_group" "allow_ssh" {
  name        = "allow-all-ssh"
  description = "Allow SSH inbound traffic"

  ingress {
    from_port   = 22
    to_port     = 22
    protocol    = "tcp"
    cidr_blocks = ["0.0.0.0/0"] # DANGEROUS
  }
}
A scanner flags 0.0.0.0/0 as a high-severity issue, pushing you to restrict the IP range to a known, trusted source.
Catch Hardcoded Secrets
Putting secrets like API keys or passwords straight into your code is a serious mistake. Once that code is committed to version control, the secret is stuck in the repository's history for good.
Insecure HCL Example:
# A hardcoded password in a variable default.
variable "db_password" {
  description = "Database admin password"
  type        = string
  default     = "SuperSecretPassword123!" # DANGEROUS
}

resource "aws_db_instance" "default" {
  # ... other configuration
  password = var.db_password
}
Scanners are good at spotting high-entropy strings and common key formats and stopping them before they're saved. Keep them in a dedicated secrets manager like AWS Secrets Manager or HashiCorp Vault.
Catch Unencrypted Data Storage
Failing to enable encryption for resources that store data, like S3 buckets or databases, can leave sensitive information vulnerable.
Insecure HCL Example:
# This S3 bucket is created without server-side encryption enabled.
resource "aws_s3_bucket" "unencrypted_data" {
  bucket = "my-company-sensitive-data-bucket"
  acl    = "private"
  # Missing encryption configuration
}
A security scanner detects the missing encryption block and tells you what configuration to add.
Which Open-Source Terraform Scanning Tools Should You Use?
There's a solid set of open-source tools that catch these and hundreds of other issues. Most are backed by commercial security companies and sit at the "core" of their larger platforms.
Here's how the leading tools compare:
| Feature | tfsec | Checkov | Terrascan | Trivy |
|---|---|---|---|---|
| Primary Focus | Terraform-Specific Security | Multi-Framework IaC Security | Multi-Framework IaC & Compliance | Unified Scanning (Containers, IaC, Secrets) |
| Backing Vendor | Aqua Security | Palo Alto Networks | Tenable | Aqua Security |
| Key Differentiator | Speed, simplicity, Terraform-native focus | Graph-based analysis for contextual awareness | Native OPA/Rego engine, drift detection | Single CLI for multiple security scanning tasks |
| Policy Language(s) | Rego, JSON, YAML | Python, YAML | Rego | Rego |
| Scans Plan File? | Yes | Yes | Yes | Yes |
How Do You Automate Security Scanning in CI/CD?
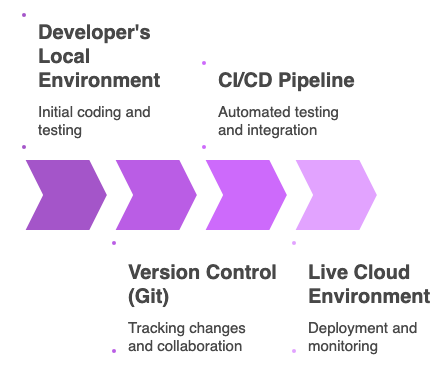
Scanning only works if it's automated. The best place to run it is your Continuous Integration/Continuous Deployment (CI/CD) pipeline, where it becomes a security gate that checks every code change.
This example runs Checkov in a GitHub Actions workflow. It runs on every pull request, scans the code, and uploads the results so they show up right on the pull request.
name: Terraform IaC Security Scan

# This workflow runs on every pull request that targets the main branch
on:
  pull_request:
    branches: [ main ]

jobs:
  checkov-scan:
    runs-on: ubuntu-latest
    steps:
      # Step 1: Check out the repository's code
      - name: Checkout code
        uses: actions/checkout@v3

      # Step 2: Set up Python, which Checkov needs to run
      - name: Set up Python 3.9
        uses: actions/setup-python@v4
        with:
          python-version: 3.9

      # Step 3: Install the Checkov scanner
      - name: Install Checkov
        run: pip install checkov

      # Step 4: Run the scan on the current directory (-d .)
      # The job will fail if Checkov finds any issues.
      # It outputs results in the SARIF format for GitHub to display.
      - name: Run Checkov scan
        run: checkov -d . --output sarif --output-file-path results.sarif

      # Step 5: Upload the SARIF file to GitHub Advanced Security
      # This step runs even if the scan fails, ensuring results are always visible.
      - name: Upload SARIF file
        if: always()
        uses: github/codeql-action/upload-sarif@v2
        with:
          sarif_file: results.sarif
Save this as .github/workflows/security_scan.yml.
Once this workflow is in place, anyone trying to merge code with a security misconfiguration gets blocked, and they see exactly what's wrong right there in the pull request.
Where Can You Learn More About Terraform Security?
These go well with this guide if you want to go further with security tooling for Terraform:
- IaC Security: Securing Your Terraform and OpenTofu Infrastructure: the pillar guide this post belongs to.
- Enforcing Policy as Code in Terraform: A Comprehensive Guide: moves from "scan to detect" to "block at the policy layer."
- CI/CD and GitOps for Terraform & OpenTofu: where scanning sits inside the broader plan/apply/approve flow.
- Terraform Drift Detection and Management: A Comprehensive Guide: scanning catches code-level issues, while drift detection catches runtime divergence.
- Terraform State Files Best Practices: state files are the single biggest plaintext-secret risk in most Terraform setups.
- What is OpenTofu?: every scanner here works against OpenTofu identically.
Key Sources Used
1. https://www.redhat.com/en/topics/devops/what-is-devsecops
2. https://www.paloaltonetworks.com/cyberpedia/what-is-cloud-security-posture-management
3. https://developer.hashicorp.com/terraform/language/manage-sensitive-data
About the author
CEO at Scalr
Sebastian Stadil is the CEO of Scalr with 15+ years of DevOps experience. He started with AWS in 2004 and advised early Microsoft Azure and Google Cloud.
Part of this guide
15 sheets
IaC Security: Securing Your Terraform and OpenTofu Infrastructure
- Terraform Module Supply Chain Attacks: Tag Mutation, Pwn Requests, and How to Pin Safely
- Malicious Terraform Providers: Supply Chain Risks and How to Verify What You Install
- Terraform Supply Chain Attacks: Risks, Real Incidents, and How to Defend Against Them
- Terraform Wiz: How to Scan, Secure, and Enforce Policy on Your IaC
- Secrets in Terraform State: Why They Leak, and the Fix
- Bring Your Own Key (BYOK): Customer-Managed Encryption for Terraform Platforms
- Streamlining AWS IAM Role Creation with Terraform: A Practical Guide
- Using Checkov with Terraform - Integrations, Features, Examples
- Bridgecrew Terraform: Pricing, Use Cases, Best Practices & Alternatives
- A Guide to Terraform Audit Logs
- How to Use Snyk with Terraform: Securing Your Infrastructure as Code
- Using Scalr Hooks with Bridgecrew Yor
- Automating Terraform Security in Scalr Deployments with Regula